Play is serious business.
At Font Awesome, we call our company retreats “Snuggles” (yes, seriously).
Why? Because ridiculousness builds trust — and great software / design.
🎧 Full story in the new episode → www.podcastawesome.com/2092855/epis...
A versioned archive of posts from Bluesky, Mastodon, GitHub, npm, YouTube, Hacker News, and blogs. See the most popular posts.
Last built .
| Since | posts | replies | likes | reposts and quotes | views | |
|---|---|---|---|---|---|---|
| Bluesky | 670 | 761 | 4,245 | 920 | ||
| Mastodon | 358 | 509 | 2,144 | 930 | ||
| npm | 56 | 465 | 889,066,549 | |||
| YouTube | 31 | 847 | 28,872 | |||
| Blog | 63 | |||||
| Podcast | 93 | |||||
| Hacker News | 6 | 311 | 384 | |||
| All | 1,430 | 1,581 | 7,620 | 1,850 | 889,095,421 |
Play is serious business.
At Font Awesome, we call our company retreats “Snuggles” (yes, seriously).
Why? Because ridiculousness builds trust — and great software / design.
🎧 Full story in the new episode → www.podcastawesome.com/2092855/epis...
CommonJS? ESM? TypeScript? Wait, even CommonJS TypeScript?? Eleventy can run them all.
Which should you choose? It depends! The social-media sized answer is: ESM 😅
Thankful to Jack Lo Russo for their 11ty docs contribution detailing how to use @deno.land’s new `dx` command with Eleventy: www.11ty.dev/docs/javascr...
Ever get your site launch-ready, only to find out your icons are ruining your speed score? We see you 👀
Check out our tips for optimizing Font Awesome icons for ultimate performance.
👉 blog.fontawesome.com/optimize...
Coming to a canary near you: support for Node’s Module Compile Cache (existing Node 20+ minimum is unchanged but this is featured tested and available in Node 22.8+ only).
Eleventy Core Dependency Watch (2025 Edition)
v4.0.0.alpha.6 (compared with v3) reduces:
1️⃣ dependencies 21.6%
2️⃣ 3rd-party dependencies 27.6%
3️⃣ node_modules weight 33.3%
New core pre-release: v4.0.0-alpha.6
Note: this includes a new `@11ty/nunjucks` package.
Humor, humility, and nerdery:
Not your typical corporate values.
But they’re key values that built Font Awesome.
This week’s Podcast Awesome is a peek behind the scenes at our actual culture — snuggles, snack projects, FARTS (yep), and all.
Listen here → www.buzzsprout.com/2092855/ep...
👥 Tired of sharing your Font Awesome Pro license like it’s a secret streaming service account? Meet Teams: the smarter, smoother way to collaborate without the chaos.
Add teammates, assign roles, and keep your icons flowing!
Watch the screencast on using teams → youtu.be/j5AhooyKlEM?...
💡 New episode: Defining Nerd
Nerdery isn’t about lone geniuses in dark basements.
It’s about people obsessed with making things better, together.
Watch here → youtu.be/Qf6kt2X0-Gc?...
Listen here → www.buzzsprout.com/2092855/epis...
Font Awesome Pro isn’t just for solo flyers — you can build a team that iconifies together.
In our latest screencast, we show you how to:
→ Add users
→ Assign roles
→ Share seats (the legal kind)
→ Avoid access chaos
💻 Watch here: youtu.be/j5AhooyKlEM?si=1igKA...
Strangers by *SPRING (I am so sorry)
Strangers by String is #BuiltWithEleventy by @likethecolour.red and @strange.website 🏆🏆🏆
"Icons won't change the world … but good people might." New episode of Podcast Awesome drops today. This one’s all about inclusive nerdery and building company culture that actually means something.
📹 Watch → youtu.be/Qf6kt2X0-Gc?...
New core pre-release: v4.0.0-alpha.5
Full release notes: github.com/11ty/elevent...
Maintenance update: to simplify our docs footprint, we will maintain historical versioned branches of our docs for *major* versions only:
v2.11ty.dev
v1.11ty.dev
v0.11ty.dev
Previously hosted minor version subdomains (e.g. v0-12-0.11ty.dev) will redirect to their respective major version.
Thanks!
What happens when you follow your curiosity across oil painting, filmmaking, 3D art, AND metal music? 🤘
You get Andy Maier. 🧠🔥
Tune into the newest episode of Podcast Awesome!
Watch here → youtu.be/IpgwIf0vqXQ?si=ufZgH...
Listen here → www.podcastawesome.com/209285...
This year we’re thankful for everyone that took a few minutes to fill out our 8 question survey (with 5 multiple choice questions 😅).
If you haven’t yet, we are still accepting submissions! It will help us prioritize the future of our project! Appreciate y’all!
In this episode of Podcast Awesome, we sit down with the founder of SOON Agency to talk about:
🎨 How oil painting makes you a better designer
🎸 Turning a band dream into a record deal
Watch here → youtu.be/IpgwIf0vqXQ?si=Rw4TN...
Listen here → www.podcastawesome.com/209285...
Update: at time of writing Eleventy core (0.x, 1.x, 2.x, 3.x, 4.x prereleases) and our official plugins are still unaffected.
(Compromised package count was updated to 834 from 533 in the latest @socket.dev update)
⚠️ Major Update on the Shai Hulud v2 campaign:
We’ve confirmed 834 malicious packages and now see spillover into Maven Central. The package org.mvnpm:posthog-node:4.18.1 contains the same Bun-based payload used in the npm compromise.
Updated analysis →
socket.dev/blog/shai-hu... #Java
“Curiosity is the compass.”
🎙️ Filmmaker Andy Maier joins us on #PodcastAwesome ! He talks:
🎥 Visual storytelling
🎸 Heavy metal, filmmaking & design
🎨 Oil painting + compositing secrets
🧠 How to pull clients in without pushy sales
📺 Watch: youtu.be/IpgwIf0vqXQ?si=0_9xi...
There is an ongoing npm security event.
At time of writing, Eleventy core and our official suite of plugins are unaffected.
🚨 A new wave of the Shai-Hulud supply chain attack has hit npm, impacting packages across widely used projects from AsyncAPI, ENS, Postman, PostHog, and Zapier. Attackers added a malicious preinstall script following account compromise. The investigation is ongoing:
What’s better than a full-featured Figma file?
A future where you don’t need one. 😎
Lindsay + Cory dream big in the latest Podcast Awesome:
🧩 Figma theming plugins
🧪 Prototyping with actual code
Designers: meet your future-friendly toolbox → youtu.be/MiNQNUFlrcU?si=yS1mV...
Final hours: 20% off for the lifetime of your Web Awesome Pro subscription. But it ends tonight, so last chance to lock it in!
👉 webawesome.com/?utm_source=bl...
Help guide the future of Eleventy by participating in the Eleventy Community Survey (and Suggestion Box)
@bobmonsour.com is looking for feedback on 11tybundle.dev — please participate in the redesign survey:
Copy, paste, ship.
Web Awesome’s patterns save you hours and your sanity.
Watch here → youtu.be/MiNQNUFlrcU?...
Listen here → www.buzzsprout.com/2092855/epis...
⏳ Heyo! Time's running out to get 20% off for life on Web Awesome Pro. This once-in-a-lifetime deal ends November 19.
From building robots with 3rd graders 🧠 to debugging at MIT 🤖 to shipping software at Font Awesome 🧰 — the lesson is the same: Simplicity wins. Every time.
#Simplicity #StartupTips #UXDesign blog.fontawesome.com/lego-lea...
⚡ From concept to current — Web Awesome is ready to roll. ⚡ Build and design faster than ever.
20% off for life ends Nov 19 — final lifetime deal 👉 webawesome.com?utm_source=b...
#WebAwesome #Frontend #OpenWeb #LifetimeDeal
Theme your entire UI without touching CSS?
Yes. Web Awesome’s Theme Builder is that slick.
🎧 Hear how it works:
Watch here → youtu.be/MiNQNUFlrcU?si=NCeSd...
Listen here → www.buzzsprout.com/2092855/ep...
#WebAwesome #DesignSystems #CSSIsHard #ThemeBuilder
🎙️Just dropped! Lindsay & Cory from Web Awesome chat about:
🛠 Making the theme builder powerful
⚡ Balancing usability + design
🧩 Figma files, MVP vibes, and real feedback
Watch here → youtu.be/MiNQNUFlrcU?...
Listen here → www.buzzsprout.com/2092855/epis...
When folks attempt to use the `eleventy` package instead of the canonical `@11ty/eleventy`, we’ll throw a helpful error now.
Thanks to the donation of the `eleventy` name on npm!
True or false:
🧪 WordPress plugin conflicts are just part of life.
FALSE.
The new Font Awesome plugin injects SVGs right into post content, meaning fewer conflicts and more icon power.
Listen here→ www.podcastawesome.com/2092855/epis...
Watch here → youtu.be/Hyx1etpMOYs?...
⚡ We flipped the switch, and the results are awesomely shocking. ⚡
Web Awesome is here — faster, smarter, and ready for whatever you build next.
Get 20% off for life on Web Awesome Pro before Nov 19 → webawesome.com/?utm_source=bl...
You know what’s cooler than icons in your WordPress block editor?
🔮 Icons you can actually see while editing.
The new version of our plugin is finally what-you-see-is-what-you-get. WYSIWYG dreams do come true, folks.
🎧 youtu.be/Hyx1etpMOYs?...
#WordPress #Gutenberg #WebDev
🎙️ Just dropped: our newest Podcast Awesome episode, where we go full nerd-mode on the all-new Font Awesome WordPress Plugin. SVGs, visual editing, fewer conflicts, and yes — Actual Human™ support.
Watch here → youtu.be/Hyx1etpMOYs?...
#WordPress #FontAwesome #OpenWeb
How we use GitHub Issues and how that’s changing: www.11ty.dev/blog/github-...
In pt. 2, Dan talks about how a weird orange peeler became the most replied-to topic in his newsletter.
Why? Because specificity is relatable.
🍊 Tiny details = big joy.
Watch here → youtu.be/DlTZBx1zyjs?si=MhTKQ...
Listen here → www.buzzsprout.com/2092855/ep...
Inside the lab, we’re already scheming what’s next. 🧠
Web Awesome is only the first phase of the experiment — and the results are already electric. ⚡
But there's still time to get in on 20% off for life on Web Awesome Pro before the offer closes Nov 19 → webawesome.com?utm_source=b...
Wondering why your Kit pageviews are mysteriously high?
In Part 1 of our "Doing More with Font Awesome" series, we cover how to:
→ Understand and track Kit usage
→ Identify where those views are coming from
→ Lock it down like a domain wizard 🔐🪄
🎥 Watch the screencast! youtu.be/frdlstifJIQ?...
🧠 What if the secret to creativity is... misspelling words?
In Ep 2, Dan Cederholm joins us again to talk about:
→ Naming fonts “Turbo” (but make it wrong on purpose)
→ Puppets, orange peelers, and imposter syndrome
The lab smells of victory (and a bit of ozone). ⚡
Web Awesome is alive, stable, and it's all systems go to build awesome stuff.
💥 20% off for life on Web Awesome Pro — extended through Nov 19.
webawesome.com?utm_source=b...
⚡ IT’S ALIVE! ⚡
Web Awesome has escaped the lab — and to celebrate, we’re offering 20% off for life on Web Awesome Pro.
This is the final lifetime deal before it vanishes forever.
Ends Nov 19 → webawesome.com?utm_source=b...
#WebAwesome #Frontend #OpenWeb #LaunchDay
No tricks here. 🎃
Just wicked-good treats! 🍬 Fast, flexible, open-source web magic.
Web Awesome — launching tomorrow!
#WebAwesome #OpenWeb
Our final experiments are in. Results:
⚙️ Faster performance
🫧 Cleaner components
🎨 More awesome
Web Awesome — certified alive (almost). ⚡
#WebAwesome #OpenWeb
✨ ICYMI: Font Awesome 7 is HERE ✨
✅ Cleaner icons
✅ 7+ Pro+ styles (hi, Notdog 🐶)
✅ Faster load times
✅ Over 1M Icon Wizard customizations
Upgrade your icons. Upgrade your life.
👉 blog.fontawesome.com/upgrade-to-f...
#FontAwesome7 #IconGlowUp #FrontendDev #FA7Launch #DevTools
Web Awesome is, and always will be, free and open source.
We offer a Pro option to sustain the open source project. Pro gets you professionally designed themes, curated color palettes, an ever-expanding pattern library, a theme builder, a powerful CDN, and much more!
Fall cleaning > spring cleaning. 🍁
We’re squashing bugs, polishing components, and prepping Web Awesome for its big debut. Stay tuned! 👀
#WebAwesome #OpenWeb #WebComponents
The breakup’s over — designers and developers are building together again. 💞
Web Awesome’s public launch brings Projects + a Figma Design Kit to make collaboration a monster mash, not a monster mess, and it's coming soon! 🧪
The Web Awesome Pro CDN makes creating, hosting, and updating your projects easier than ever!
Here's a sneak peek at what's coming next week…
Something's coming very soon ...
🍂 The leaves are turning, the code is tightening, and something awesome is bubbling in the lab.
Web Awesome is almost alive. ⚡
#WebAwesome #OpenWeb #WebComponents
🍂 The leaves are turning, the code is tightening, and something awesome is bubbling in the lab.
Web Awesome is almost alive. ⚡
#WebAwesome #OpenWeb #WebComponents
Lost in your website's maze? 🐂
Web Awesome's <wa-breadcrumb> component is your simple, customizable guide. Drop it in and keep users on track like Theseus.
What's your site's trickiest path?
“Type design is like solving a little puzzle. It’s small, satisfying, and contained. Like making icons.” — Dan Cederholm 🧠
🧩 Puzzle brain = creative fuel
🎥 Watch here → youtu.be/PUXK-yB3LEM?...
🎧 Listen here → www.buzzsprout.com/2092855/epis...
#DesignThinking #CreativeWork #FontNerdsUnite
Behold the eerie brilliance of <wa-skeleton>! 💀
This open source component stands in for content while the page loads. Dare to weave it into your site?
Show us your Web Awesome magic!
Dan Cederholm:
✔️ Wrote a book on CSS (literally)
✔️ Co-founded Dribbble
✔️ Made a typeface inspired by a bank alarm sign
✔️ Designed fonts, dice, T-shirts, newsletters
… and finally found what he wants to do at 51.
🎧 Watch it → youtu.be/PUXK-yB3LEM?...
#CreativeCareer #SimpleBits #DesignPodcast
"Promotion is hard. Everyone’s doing the same things. You have to actually enjoy what you’re doing."
Dan talks about learning for the sake of learning — and how trying weird new things keeps your work fresh 💡
🎧 Ep. 1 is live: www.buzzsprout.com/2092855/ep...
#CreativeCareer #DesignPodcast
No tricks…all treats! The initial version of Web Awesome Pro's Figma file is coming later this month! 🎃
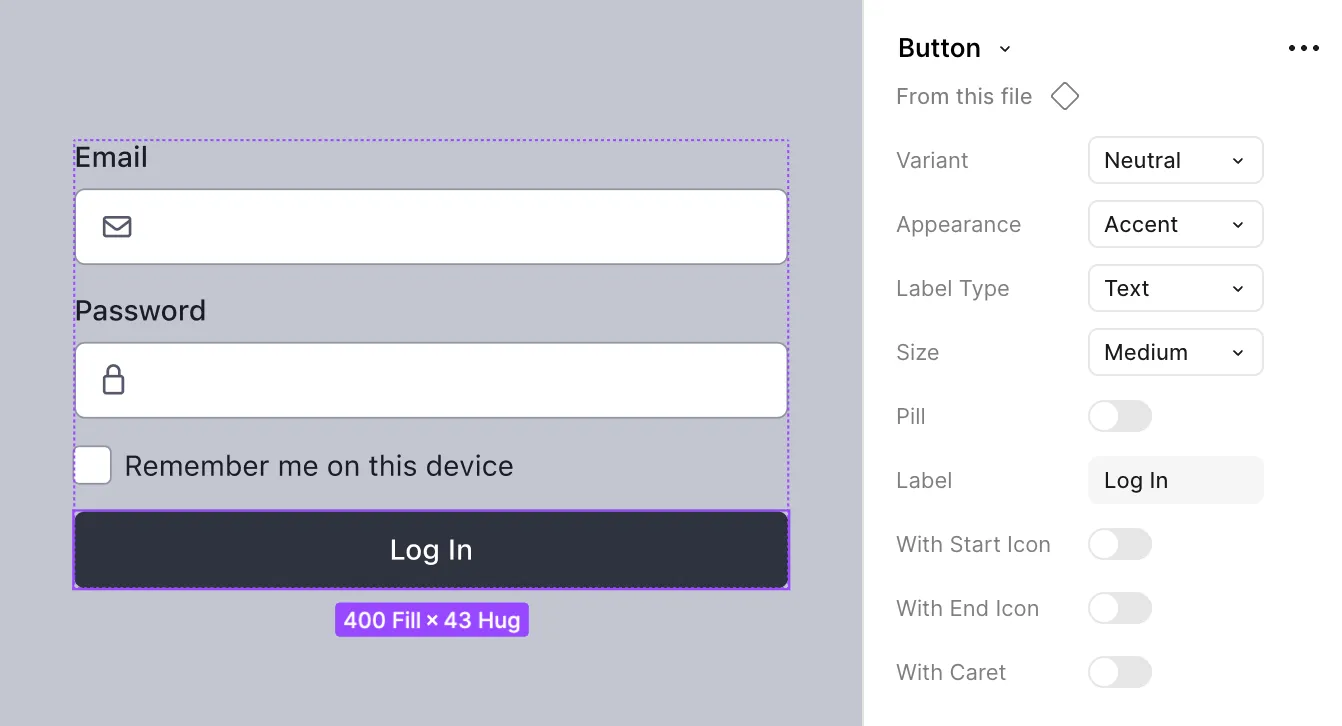
"Promotion is hard. Everyone’s doing the same things. You have to actually enjoy what you’re doing." Dan talks about learning for the sake of learning — and how trying weird new things keeps your work fresh 💡
🎧 Ep 1. with Dan is live: www.buzzsprout.com/2092855/epis...
#CreativeCareer#DesignPodcast
At 12:00pm ET, the Web Awesome website will be offline briefly for scheduled maintenance. We expect this to take less than an hour.
Thanks for your patience as we prepare for launch later this month!
Dan Cederholm (yes, THAT Dan) joins us to talk about fonts, merch, creative freedom & why you should definitely spend more time NOT doing your job.
This one’s for the late bloomers, font nerds, & makers of weird things. 🧠🎲👕
Listen here: www.podcastawesome.com/209285...
#FontAwesome #SimpleBits
@peruvianidol.com can the community sponsor the 11ty.recipes domain?
Every Web Awesome theme comes with dark mode built-in 🌛
This is the correct way to read them 👇
Everyone reads @webawesome.com element names like they are Wario in their head right? <wa-button></wa-button> is Wah!-button
🧷 Clippy: from annoying UI pop-up to nostalgic legend
This week on Podcast Awesome, we trace the legacy of Microsoft’s googly-eyed assistant and what he means for modern UX.
🎥 Watch here → youtu.be/sXuFnrPOkuc?si=Hsglw...
🎧 Listen here → www.buzzsprout.com/2092855/ep...
🧷 Clippy: from annoying UI pop-up to nostalgic legend
This week on Podcast Awesome, we trace the legacy of Microsoft’s googly-eyed assistant and what he means for modern UX.
🎧 www.youtube.com/watch?v=sXuFn...
#PodcastAwesome #ClippyCult #DigitalDesignHistory #TechFolkLore #MicrosoftDesign
Missed our Eleventy episode with Zach & Konnor?
We cover:
✅ Static vs dynamic
✅ How to add auth to your docs
✅ Why open-source still wins
🎧 Catch up now: youtu.be/0SKA5vE7d88?...
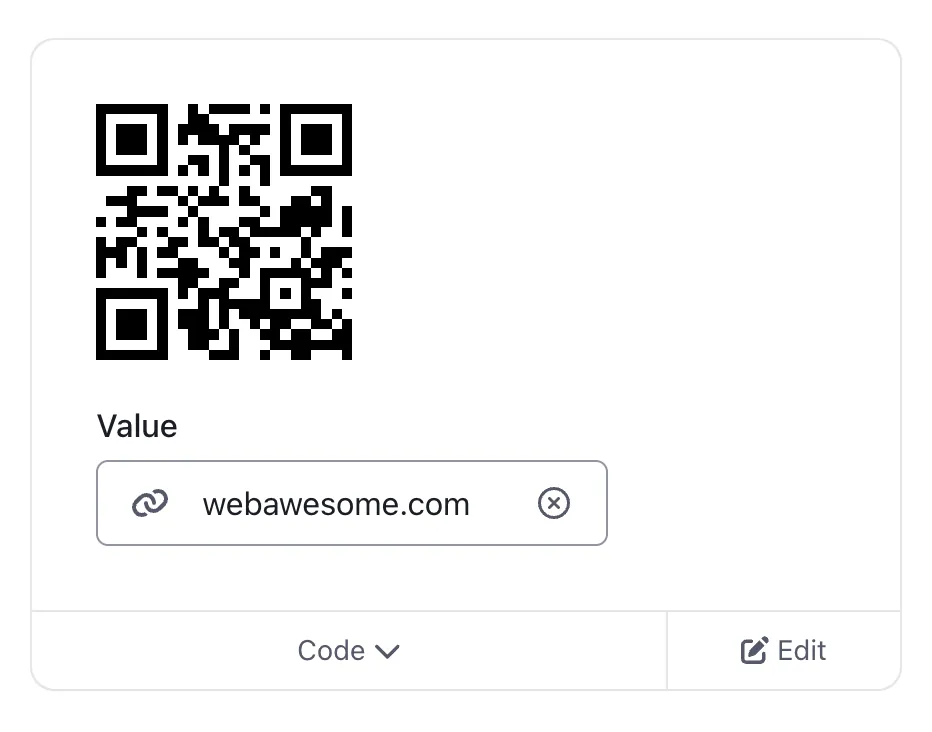
Generating QR codes has never been easier!
<wa-qr-code
value="webawesome.com"
label="QR code linking to webawesome.com"
>
</wa-qr-code>
Animate elements declaratively with nearly 100 baked-in presets, or roll your own with custom keyframes with <wa-animation>
Still thinking about this gem from @zachleat on build-time confidence:
“You catch errors before they hit production—and your users never see it.”
If that doesn't make you love static sites again, nothing will.
🎧 Watch it → youtu.be/0SKA5vE7d88?...
Sometimes you need an icon set that just works without stealing the spotlight — and FA Utility is here to help. With a Bauhaus-inspired blend of sharp corners and smooth curves, this pack fits seamlessly into any project and gets the job done.
Get it now: fontawesome.com/plans/pro-pl...
Use <wa-intersection-observer> to easily add classes to elements when they appear in the viewport. No JavaScript required!
Eight new icon packs?
Great work, @fontawesome.com! 🫡
7 new Icon Packs isn’t cool. You know what is? 8 new Icon Packs!
FA Utility is hot off the presses! To celebrate this release, you can get a 20% off discount on the first year of a Pro+ subscription and see what all the fuss is about!
Grab it now: fontawesome.com/plans/pro-pl...
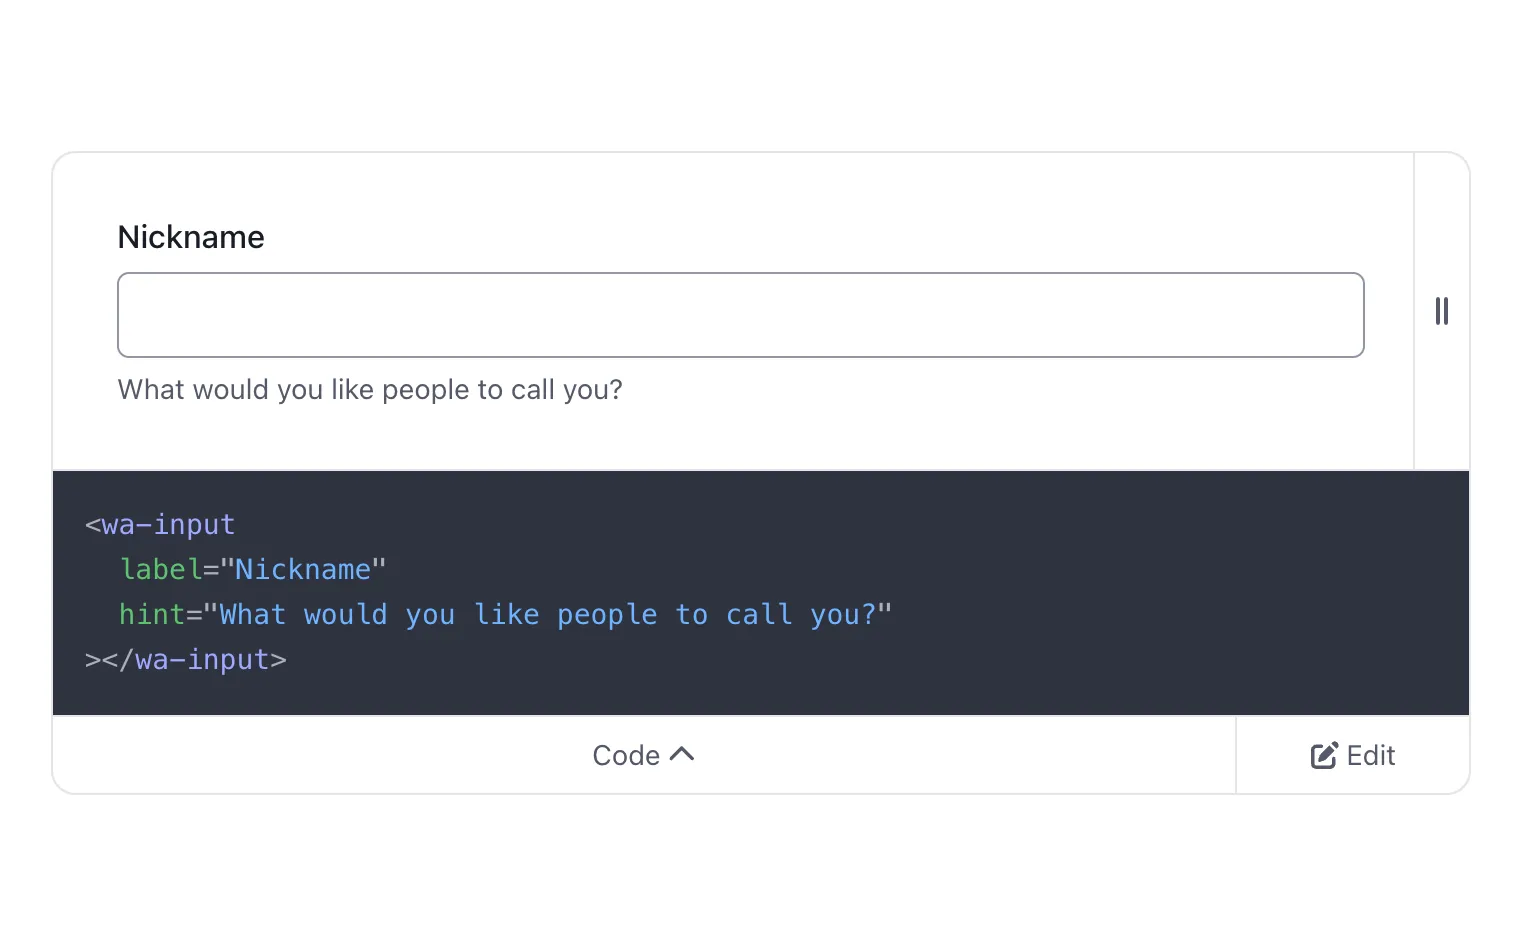
Web Awesome bakes accessibility in!
Form controls automatically wire up their labels and hints under the hood, allowing you to write cleaner HTML with less chance for error. 💪
7 new Icon Packs isn’t cool. You know what is? 8 new Icon Packs!
FA Utility is hot off the presses! To celebrate this release, you can get a 20% off discount on the first year of a Pro+ subscription and see what all the fuss is about!
Grab it now: fontawesome.com/plans/pro-pl...
How do you add pro-only content to a static site…
...without turning your build into a mess?
Hint: It involves a bit of Express and a lot of Eleventy.
🎧 youtu.be/0SKA5vE7d88?...
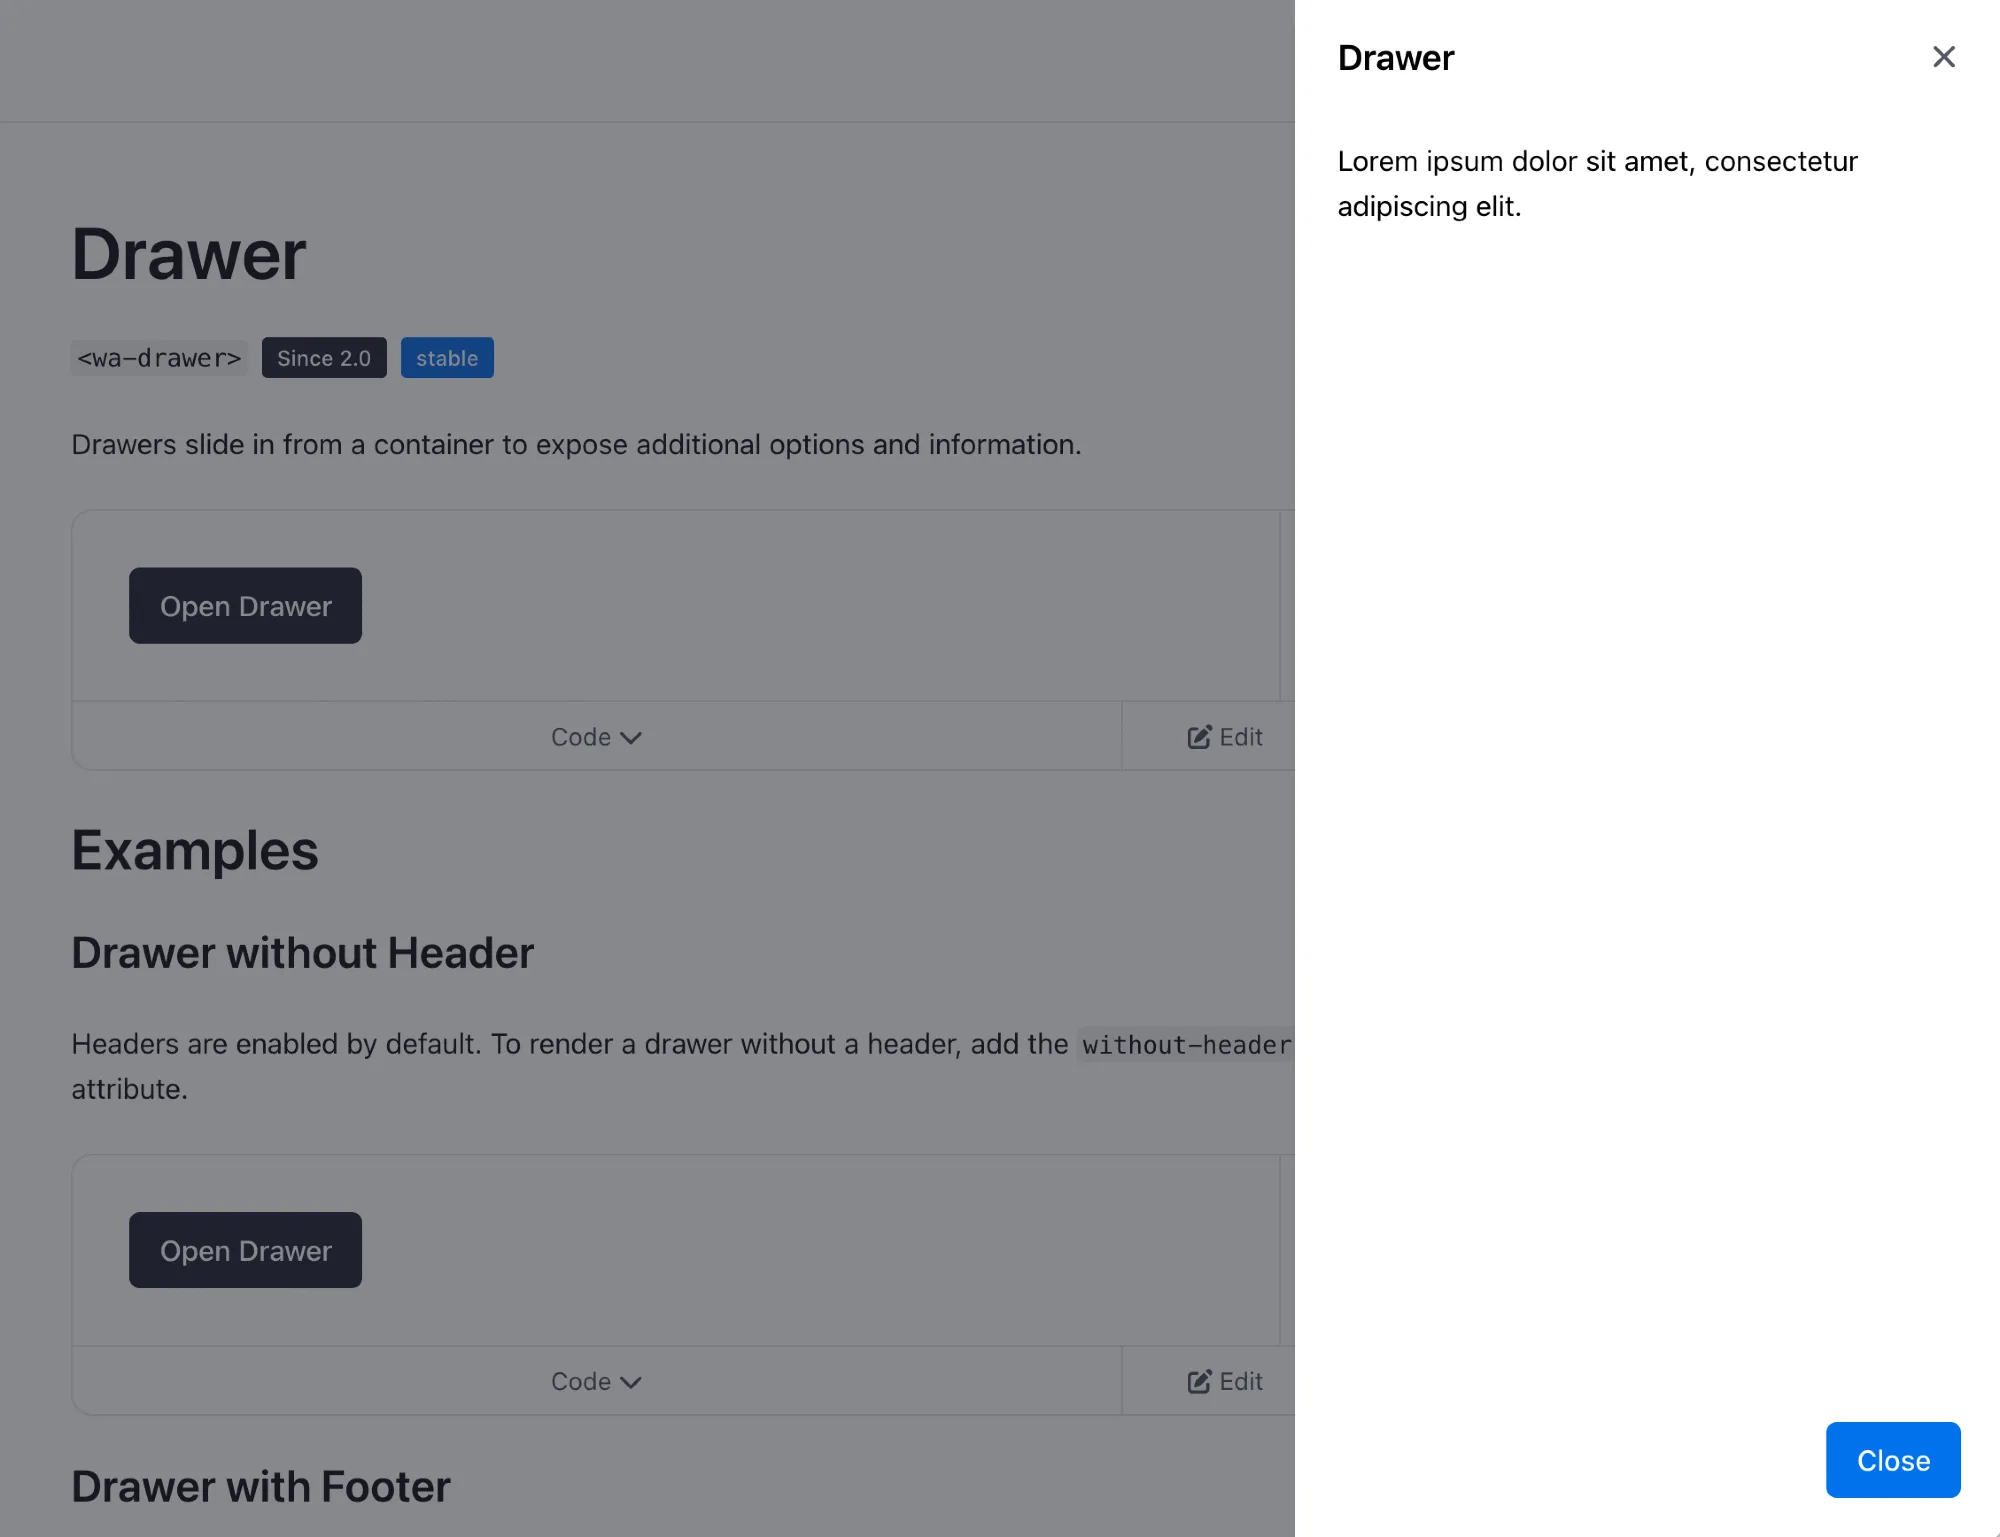
Web Awesome makes drawers easy. And with declarative invokers, you can open and close them without writing any JavaScript.
The best dev tooling balances simplicity and power.
This week’s podcast unpacks how Eleventy helps Web Awesome do just that—with zero vendor lock-in.
🎧 Tune in: youtu.be/0SKA5vE7d88?...
“We wanted auth. We didn’t want bloat.”
Web Awesome's Konnor Rogers explains how Web Awesome kept docs dynamic without ditching Eleventy.
🔗 youtu.be/0SKA5vE7d88?feature=...
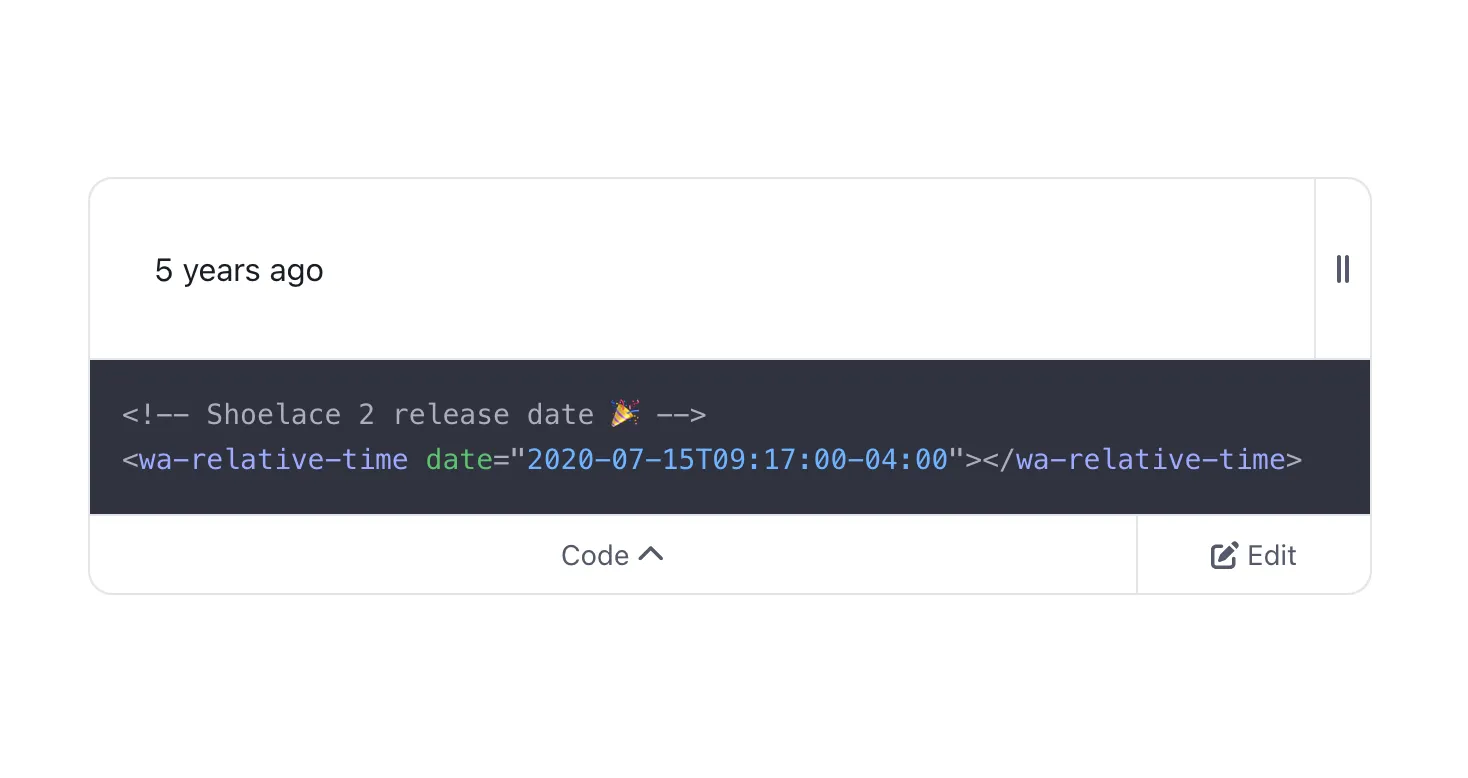
Format relative times like a champ with our declarative wrapper around the platform's Intl.RelativeTimeFormat API.
webawesome.com/docs/compone...
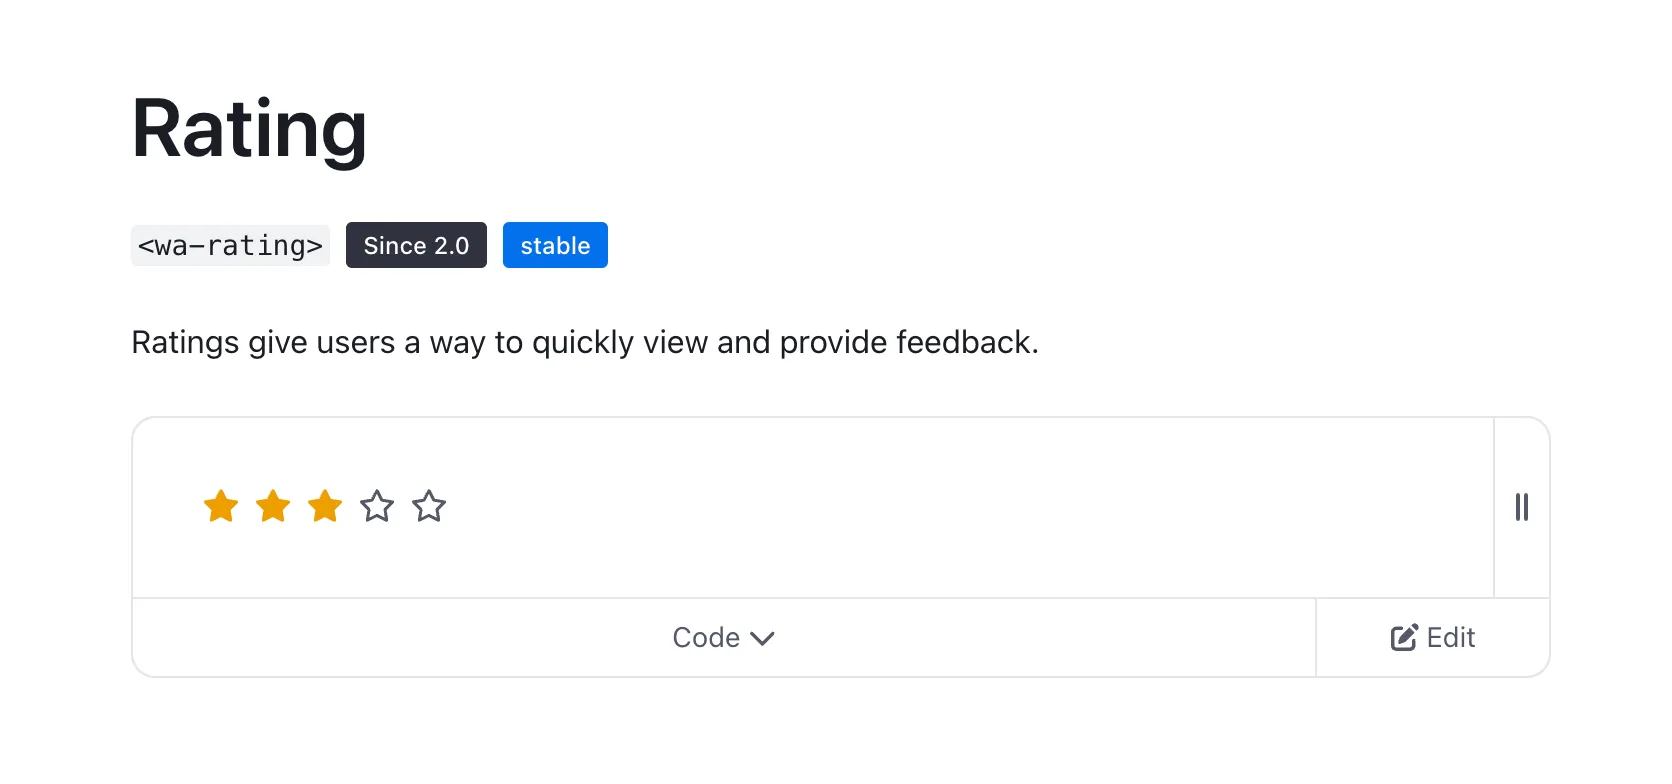
🌟 Add user feedback to your app with ease!
The <wa-rating> component lets you customize ratings with labels, precision, sizing, custom icons, and more.
Check out the docs and make your UI shine! 📊✨
Friendly reminder that Web Awesome is — and always will be — free and open source 👑
Missed it last week?
Burton Smith joined Podcast Awesome to share how he’s building a smoother dev experience for Web Components.
📦 Tooling
📚 Docs
💡 Ideas
🎧 Replay it → www.buzzsprout.com/2092855/epis...
#WebComponents #PodcastAwesome #DXMatters
“The better the DX, the more people stick around.”
— Burton Smith
If you’ve ever wrestled with Web Components and wished they worked like framework components…
This one’s for you.
🎥 Watch here → youtu.be/o6ygtiP31ws?...
🎧 Listen here → www.buzzsprout.com/2092855/epis...
#WebComponents
Did you know? An Eleventy icon is now available (for free!) in Font Awesome v7: fontawesome.com/icons/eleventy
Use it today with the newly released stable v1.0.0 of the Font Awesome Eleventy plugin: github.com/11ty/elevent...
🔥 Developer take:
Declarative Shadow DOM isn’t the final solution.
Burton Smith shares why Declarative Custom Elements might be the future.
🎧 Full convo → youtu.be/o6ygtiP31ws?feature=...
#PodcastAwesome #WebComponents #DeclarativeDesign
🧙 Web Components need better tools.
Burton Smith built them.
🎧 Full ep → youtu.be/o6ygtiP31ws?...
#ToolingFixes #DXLove #PodcastAwesome
🎧 New Podcast Awesome episode!
What do you get when you mix:
🛠️ An open source wizard
💡 A pile of DX friction
🤯 And a dream of seamless Web Components?
You get Burton Smith’s Web Components Toolkit.
▶️ youtu.be/o6ygtiP31ws?...
#WebComponents #DXMatters #PodcastAwesome
Make sure you follow @socket.dev to see the latest in JS supply chain security (we’ll update you if any reports affect Eleventy!)
Some good practices to help mitigate in your projects:
1. Use `npm install --ignore-scripts` (or use pnpm)
2. Use `npm ci` and a package-lock.json on your build server
Update: bsky.app/profile/weba...
Web Awesome 3.0.0-beta.6 has just been published to npm.
This version is safe to use, as it pins the affected dependency to the last safe version. You can update to 3.0.0-beta.6 by running the following command:
npm i @awesome.me/webawesome@3.0.0-beta.6
Web Awesome 3.0.0-beta.6 has just been published to npm.
This version is safe to use, as it pins the affected dependency to the last safe version. You can update to 3.0.0-beta.6 by running the following command:
npm i @awesome.me/webawesome@3.0.0-beta.6
⚠️ SECURITY ALERT: An npm dependency used by Web Awesome was compromised a few hours ago.
This ONLY affects npm installs — CDN users are safe.
DO NOT install Web Awesome via npm right now. New unaffected version is publishing now…
🚨 Malicious update to @ctrl/tinycolor on npm is part of an active supply chain attack hitting 40+ packages across multiple maintainers. Audit & remove affected versions.
Our analysis of the malware: socket.dev/blog/tinycol... #NodeJS #JavaScript
Details on the affected dependency can be found here: t.co/pvhIvAA7N1
⚠️ SECURITY ALERT: An npm dependency used by Web Awesome was compromised a few hours ago.
This ONLY affects npm installs — CDN users are safe.
DO NOT install Web Awesome via npm right now. New unaffected version is publishing now…
Eleventy v4.0 Proposal: remove the data deep merge opt-out feature originally introduced to ease a breaking change for folks upgrading to Eleventy v1.
Vote with a 👍 or 👎 here: github.com/11ty/elevent...